How the Global Privacy Control Browser Signal Works
One header, one character, and a growing pile of state law behind it. Here is what Global Privacy Control sends and why websites must listen.
In this story 8 sections
Global Privacy Control is a browser setting that tells every website you visit not to sell or share your personal data. When it is on, your browser adds a one-line signal to each request. In California and about a dozen other states, covered businesses must treat that signal as a legal opt-out request.
It sounds almost too simple, and in a way it is. The signal itself is a single character. All the force behind it comes from state privacy laws, and from regulators who have started fining companies that ignore it.
Oddworldz explains the machinery behind the sites and apps you use daily. This explainer is for anyone who has clicked "Do Not Sell My Info" on site after site and wondered if there is a better way. It covers what the signal actually sends, which laws give it teeth, and what changes when California's browser rule starts on January 1, 2027.
What Does Global Privacy Control Actually Send?
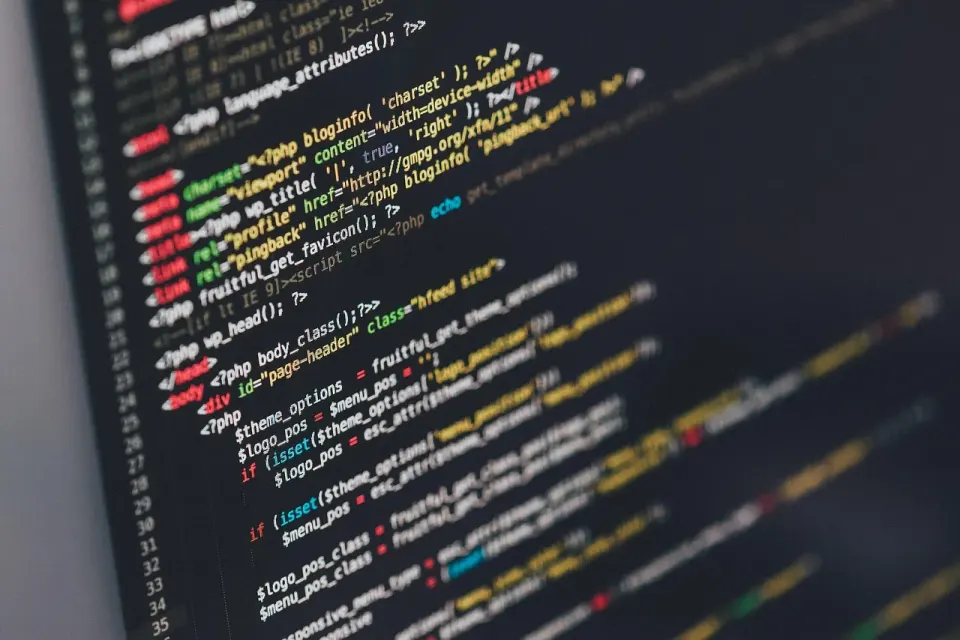
Global Privacy Control sends one short HTTP header with every page request: Sec-GPC: 1. HTTP headers are the small notes a browser attaches to each request, describing things like your language. This one says you do not want your data sold or shared. If the setting is off, the browser sends nothing.
The World Wide Web Consortium (W3C) draft specification, dated September 24, 2026, is strict about the details. The value must be exactly the character "1". Servers must ignore anything else. Network middlemen may not strip the header out.
Websites can also check the setting with a script. The W3C draft defines a simple true-or-false property, navigator.globalPrivacyControl, that page code can read. A site can even publish a small file at /.well-known/gpc.json to declare that it supports the signal.
One detail tells you how carefully the standard is written. The browser captures your preference when a page loads. If you flip the setting mid-visit, open tabs keep the old value until they reload, and the spec suggests browsers offer to reload them.
How Is Global Privacy Control Different From Do Not Track?
Global Privacy Control differs from the older Do Not Track setting mainly because laws now back it. Do Not Track also sent a one-line header, DNT: 1, starting around 2010. No law required sites to obey it, so most ignored it, and Apple dropped it from Safari in 2019.
The technical idea barely changed. What changed was the legal setting around it. Global Privacy Control was designed from the start to map onto a specific legal right, the right to opt out of the sale or sharing of personal data.
The scope is narrower, too. Do Not Track was vague about what "tracking" meant. The W3C draft ties Global Privacy Control to a clearer request: do not sell or share my data, and do not use it for targeted advertising across other sites.
That narrower request is easier to enforce. A regulator can test whether a site kept sending data to ad partners after receiving the signal. "Stop tracking me" was much harder to pin down.
What Counts as Selling or Sharing Your Data?
Under California law, "selling" is broader than handing over data for cash. It can include passing personal information to another company for anything of value. "Sharing" covers giving data to others for cross-context behavioral advertising, the ads that follow you from one site to the next.
Ad technology is where this gets tangled. When a page loads, it may send identifiers and page details to dozens of ad partners in a fraction of a second. The signal asks the site to stop those transfers for you. It does not ask the site to forget what it already holds. Deleting data you have already given is a separate request with its own process.
Why a One-Character Signal Has Legal Force
The signal matters because laws say it does. On its California Consumer Privacy Act page, the California Attorney General's office says a user-enabled global privacy control must be honored by covered businesses as a valid request to stop selling or sharing data.
That turns a polite request into an enforceable one. Under the California Consumer Privacy Act (CCPA), a business that sells or shares personal data must offer ways to opt out. For businesses that collect data online, the browser signal counts as one of those ways.
California is not alone. The California Privacy Protection Agency (CPPA) says California is one of about a dozen states that require businesses to honor opt-out preference signals. The details differ by state, but the basic idea is the same.
We would flag one honest limit here. The signal does not technically stop anything. It is like a "do not disturb" sign on a hotel door. It works because ignoring it carries legal risk, not because it locks the door. In that sense it resembles caller ID, which, as we explained in our piece on how caller ID spoofing works, is a claim the other side can choose to respect or abuse.
The Fines That Gave Global Privacy Control Teeth
Enforcement is what made companies pay attention. In 2022, the California Attorney General's first public CCPA settlement, with Sephora, involved opt-out requests sent through global privacy controls that were not processed. The penalty was $1.2 million.
A larger case followed. On July 1, 2025, Attorney General Rob Bonta announced a $1.55 million settlement with Healthline.com, the largest CCPA penalty to that date. The complaint alleged Healthline kept sharing data with advertising partners after people opted out of targeted ads.
The Healthline case shows where things usually break. Under the settlement, Healthline must make sure its opt-out tools actually work. A setting that looks right on screen can still leak data in the background if nobody tests it.
For readers, the takeaway is mixed. The signal has real legal weight. But you cannot easily see whether a given site obeys it, so enforcement depends on regulators doing the checking.
California's Browser Rule Starts in 2027
Until now, the catch has been finding a browser that sends the signal. The Global Privacy Control project site lists Brave and DuckDuckGo, which turn it on by default, and Firefox, where you enable it in settings. Others need an extension such as Privacy Badger.
California is changing that. The CPPA announced the Legislature's passage of the Opt Me Out Act (AB 566) on September 11, 2025, saying it would cover all browsers, including Google Chrome, Apple Safari and Microsoft Edge. Governor Gavin Newsom signed it on October 8, 2025, and it takes effect on January 1, 2027.
The law requires browser makers to offer a setting that sends an opt-out preference signal and to explain how it works. Browsers that do this get protection if a website then ignores the signal. The CPPA can write rules to fill in the details.
Some questions remain open. Coverage notes that the law does not spell out which signal format browsers must use, and it does not clearly address mobile browsers. Global Privacy Control is the obvious candidate, but that is a reasonable guess, not a settled fact.
Standards bodies move slowly, too. The specification was first proposed in 2020 and is still a working draft, a pace that will feel familiar to anyone who followed the long fight over the leap second.
How to Turn On Global Privacy Control Today
You do not need to wait for 2027. Here are the main ways to start sending the signal now:
- Use a browser that sends it by default. Brave and DuckDuckGo do this out of the box.
- Turn it on in Firefox. Look in the privacy settings for the option to tell websites not to sell or share your data.
- Add an extension to other browsers. Privacy Badger from the Electronic Frontier Foundation is one option.
- Keep using site-level opt-outs where it matters. The signal applies per browser, so your phone and laptop need separate setups.
Expect a few limits. Signing in to an account can link activity across devices, and the signal does not stop data you hand over directly. It works alongside other protections, such as passkeys that refuse to work on fake websites, rather than replacing them.
The Bottom Line on Global Privacy Control
Global Privacy Control is a one-character request with state law behind it. Your browser sends Sec-GPC: 1, and in California and a growing list of states, covered businesses must treat that as an opt-out. Fines against Sephora and Healthline show regulators are watching.
At Oddworldz, we think it is one of the rare privacy tools that costs nothing and takes a minute to set up. Turn it on now. By January 2027, Californians should find the option in every major browser, and the rest of the country may not be far behind.
What is Global Privacy Control in a browser?
Do websites have to honor Global Privacy Control?
Which browsers support Global Privacy Control?
Does Global Privacy Control block tracking?
In this story 8 sections
Keep Reading
All stories
The Odd List · Fridays